Which of my AI agent sessions has a secret in it?
ACTVT scans every Claude Code, Codex and Pi session on your Mac for sensitive data, such as API keys, passwords, connection strings, emails and card numbers. The scan runs on the Mac and sends nothing anywhere. The Has PII collection in the session list shows only the sessions where it found something, and you can combine it with the date filter. In a session, the values are masked by default, the inspector says what it found, and the eye button reveals them. Masking hides a key on screen, but the agent has already seen it, so rotate a key that turned up. The session browser and its filters are part of the Premium tier.
0:564 chapters
Step by step
0:00Today’s sessions
Every agent session on this Mac, newest first. Filter to today: five agents ran. Did any of them see a secret?
0:15Has PII
Has PII keeps the sessions where ACTVT found a key, a password or an email. Two did.
0:23Open it
The log I pasted had the Stripe key in it. ACTVT masks it. The scan runs on this Mac, and nothing is sent anywhere to be checked.
0:39Check, then rotate
Reveal it to see which key it was (here, a planted test key). Then rotate it: masking hides it on screen, but the agent has already seen it.
More tutorials
All tutorials →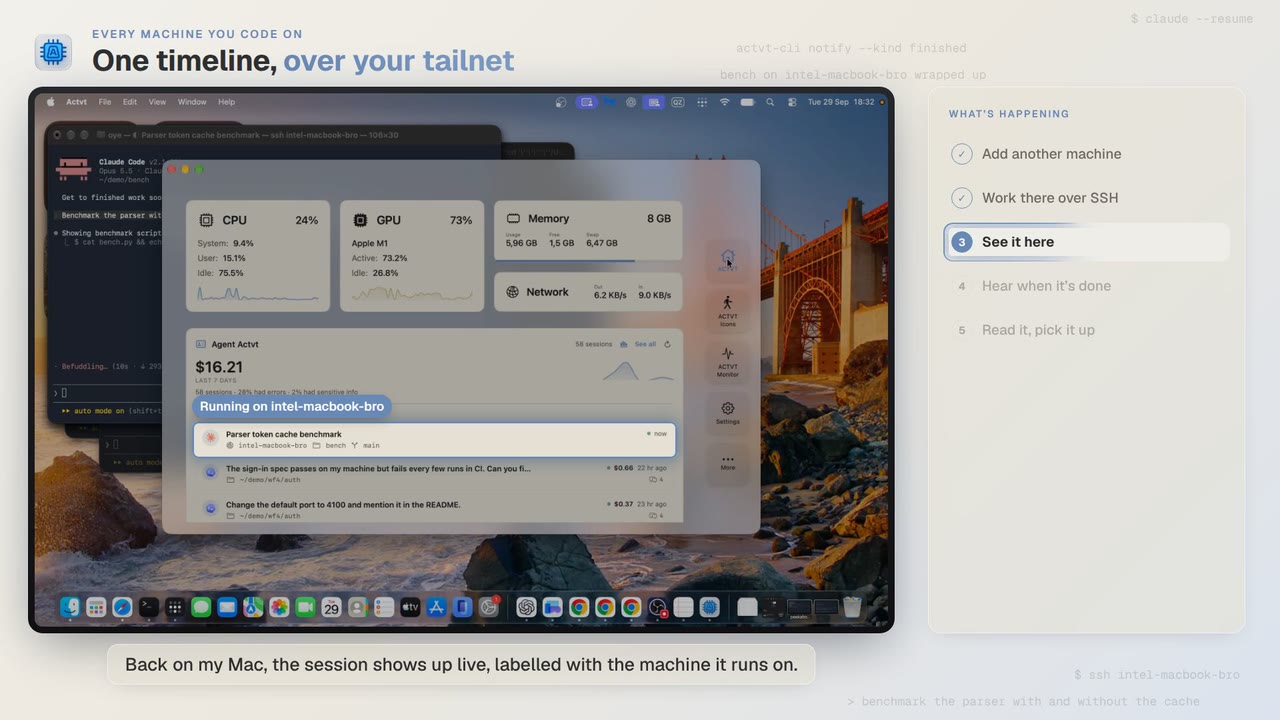 1:24
Every machine you code on
See agent sessions from all your machines over SSH
Start Claude Code on another Mac over SSH, and you can follow the session from your own Mac while it runs and read the whole transcript when it’s done.
 3:42
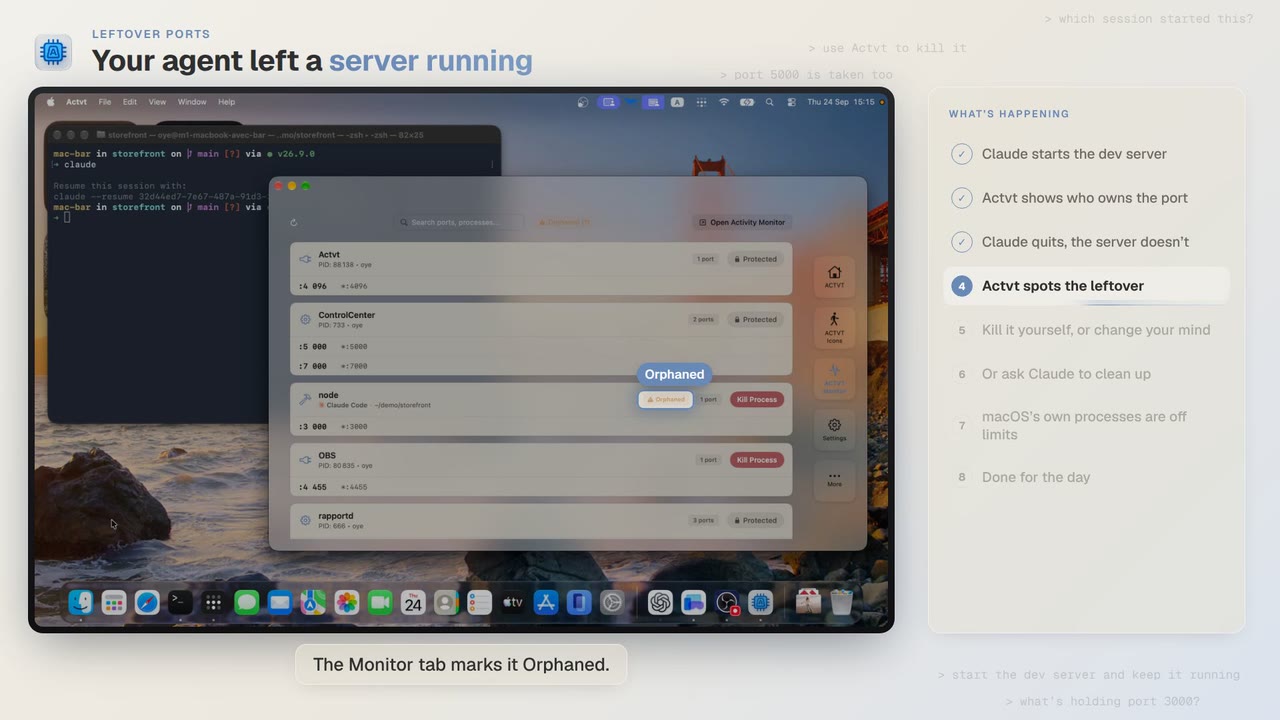
Leftover ports
Find and kill the dev server your AI agent left running
Claude Code starts a dev server and then quits, and port 3000 stays taken. ACTVT shows you the server whose session is gone and lets you free the port safely.
 0:48
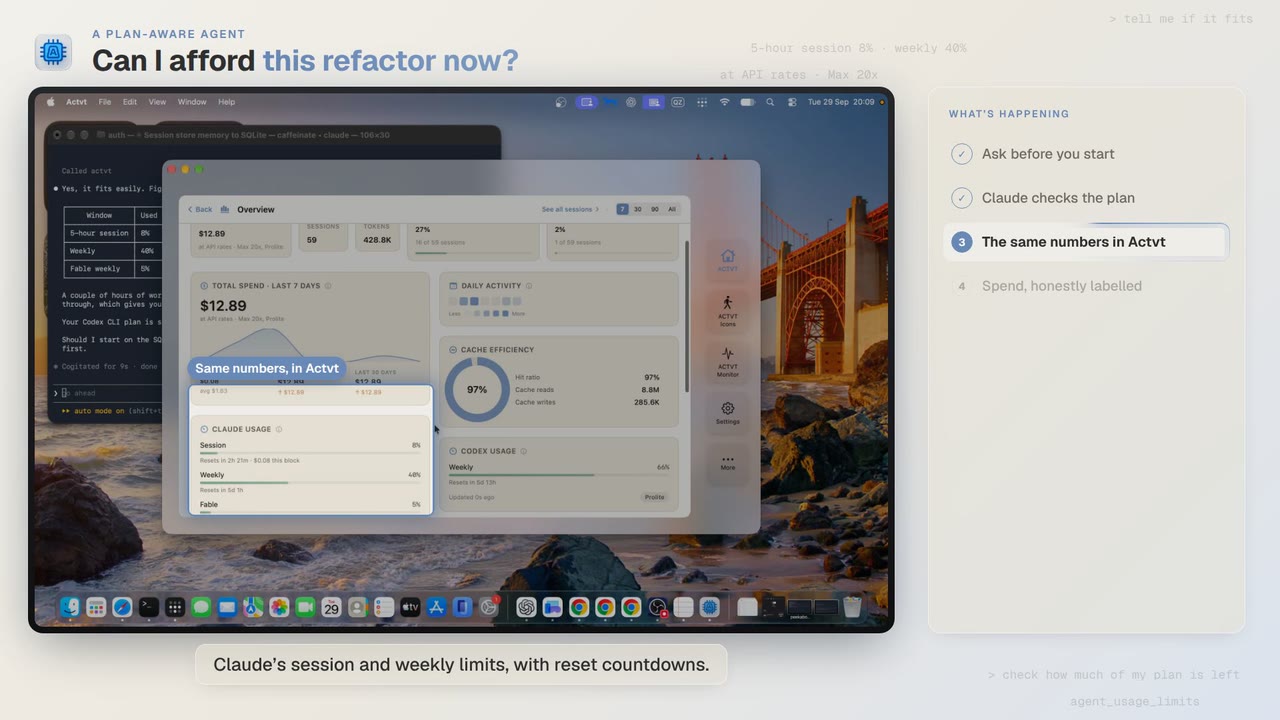
A plan-aware agent
Check how much of your plan is left before a long agent job
Before a two-hour job, Claude Code asks ACTVT how much of your plan is left. You can see the same limits in ACTVT, along with when each one resets.
Try it on your own agents
ACTVT is free to start, and reads the session files Claude Code, Codex CLI and Pi already write. Nothing to configure.